

01 · The challenge
Gaps and inconsistent results
Point-in-time tests from multiple vendors left time gaps, used different methodologies and found few high or critical vulnerabilities.
 Case Study
NOV needed more consistent penetration testing and faster access to findings. Within the first two weeks, vetted Synack Red Team researchers found exploitable vulnerabilities where previous testers had found none. With continuous testing through Synack365, NOV’s security and DevOps teams could review findings in real time, prioritize fixes, and verify patches.
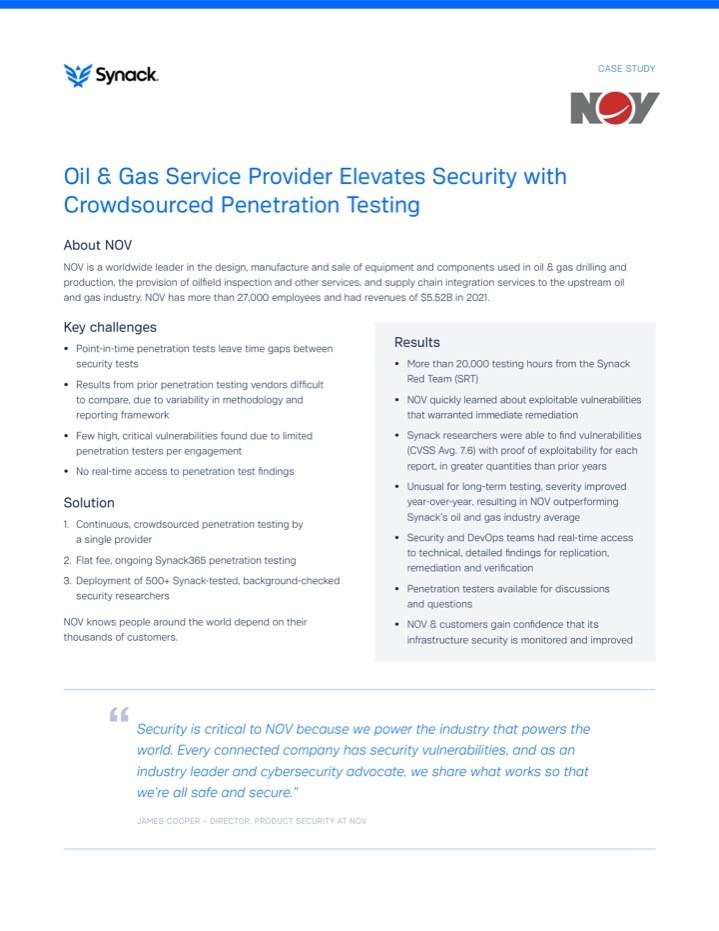
NOV powers the industry that powers the world, and it needed testing it could trust.
Point-in-time tests from multiple vendors left time gaps, used different methodologies and found few high or critical vulnerabilities.
Flat-fee Synack365 testing by 500+ vetted researchers across NOV’s websites, apps, cloud and host infrastructure.
Higher-severity findings, fewer vulnerabilities per target over time and real-time access to every result.
NOV is a worldwide leader in equipment and components for oil and gas drilling and production, oilfield inspection and supply chain integration services. At the time of the 2023 case study, it had more than 27,000 employees.
NOV had regularly tested its infrastructure using multiple penetration testing firms but had constant issues with inconsistent, limited findings. Results were hard to compare across vendors, and there was no real-time access to findings.
NOV’s security leadership was ready to try a more effective approach with continuous testing by vetted experts. According to the 2023 case study, NOV had upgraded its Synack services every year since 2018.
Before Synack, we wondered if our security system was really effective or if previous testers had simply missed the vulnerabilities, due to limited sets of pentesters in those engagements.
NOV’s entire hosted infrastructure was selected for initial testing, and in the first two weeks Synack’s team found vulnerabilities where its predecessors had found none.
Synack vets, skills-tests, interviews and background checks researchers, and removes inactive or underperforming ones.
Continuous testing from a single provider, including remediation guidance and re-testing.
Campaigns, including a NIST 800-53 Campaign, confirmed best practices were consistently in place across assets.
NOV could scope, pause and restart testing, pull reports, verify patches and monitor Attacker Resistance Scores.
“We now have greater confidence in our security because Synack showed us vulnerabilities that matter, found by their crowdsourced group of 500+ researchers, then told us what we needed to improve and how to fix it.”
NOV’s IT Security team used Synack’s findings to educate business groups about real risk, accelerating adoption of newer protective measures.
Thanks to Synack, our business groups know there are real risks of exploits, so they’re behind our protective measures and we’re resting better. Synack makes the benefits of using DevSecOps best practices very clear.
At this point, a lot of people are being more proactive and asking where they can get these protections. Synack opened some eyes and changed attitudes with the business groups that were used to traditional testing methods.
The data is available when we need it. We don’t need to call the account manager who then has to figure it out with the penetration tester. Synack’s solution and reporting is superior to anything we’ve seen in the past.
Continuous penetration testing is a key component to our Attack Surface Management program and Synack delivers!
Synack’s results and the company’s flat-fee pricing, which includes testing, remediation guidance and re-testing, confirmed Synack was the right choice for us.
Synack found exploitable vulnerabilities that warranted immediate remediation where previous vendors had found none.
High and critical vulnerabilities made up 44% of Synack’s findings, compared with the 32% typically found in the National Vulnerability Database, with proof of exploitability for each report.
Severity improved year over year. By the time of the 2023 case study, the CVSS scores of Synack’s findings for NOV exceeded Synack’s oil and gas customer average for severity of findings.
As NOV remediated and strengthened best practices, fewer vulnerabilities were found per target.
Detailed findings for replication, remediation and verification were available in real time, with testers on hand for questions.
Consistent, customizable reports demonstrated improvement over time and supported compliance reporting.
NOV is a worldwide leader in the design, manufacture and sale of equipment and components used in oil and gas drilling and production. At the time of the 2023 case study, it had more than 27,000 employees.
Flat-fee Synack365 continuous penetration testing by the Synack Red Team, along with Synack Campaigns and the secure customer portal.
NOV’s websites, apps, cloud and host infrastructure, starting with its entire hosted infrastructure and all NOV IPs.
In the first two weeks, Synack found vulnerabilities where predecessors had found none, and high and critical findings made up 44% of results.
Customizable reports were used for compliance reporting, and a NIST 800-53 Campaign helped confirm best practices were in place across assets.
Read how NOV moved to continuous penetration testing with vetted experts, identified exploitable vulnerabilities, and used real-time findings to guide remediation.
 Case Study · IT services and training How FDM Group Turned Pentest Findings Into Fixes Read the FDM Group story →
 Case Study · Travel technology How Sabre Builds Human-Led API Security Testing into Its Development Cycle Read the Sabre story →
 Case Study · Financial services How Varo Bank Used Continuous Pentesting to Demonstrate Security Readiness Read the Varo Bank story →