

01 · The challenge
Reports with little to act on
Pentests from multiple vendors affirmed a strong position but offered limited information and little to mitigate.
 Case Study
FDM Group needed pentest reports that showed its teams what to fix. Vetted Synack Red Team researchers tested its web applications, host and cloud assets, and APIs. Detailed reports and direct access to testers helped developers reproduce vulnerabilities and gave the security team evidence to prioritize fixes.
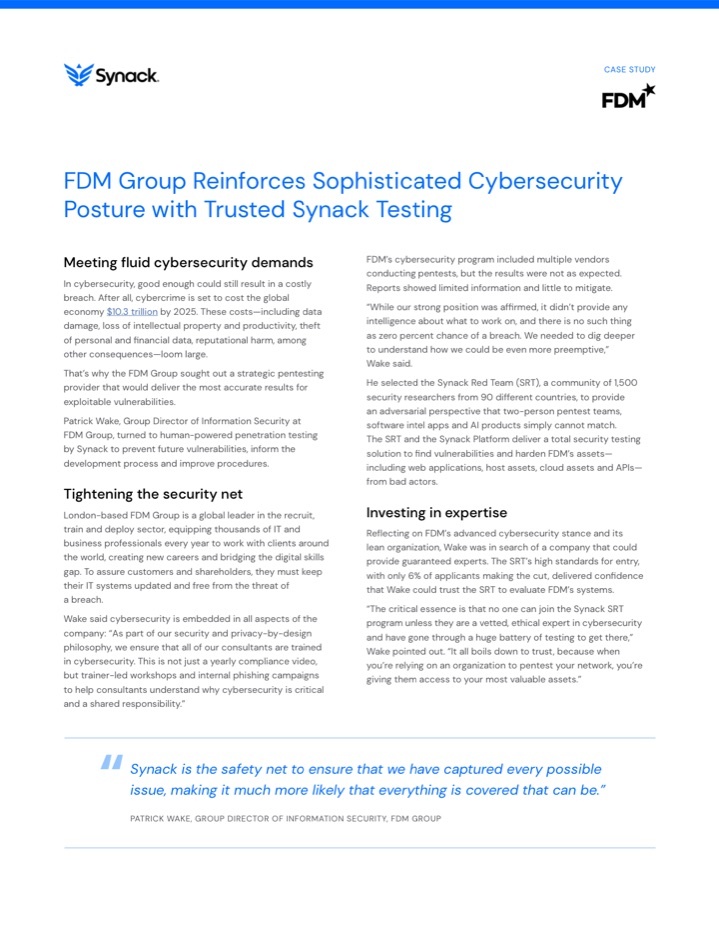
Being strong was not enough. FDM wanted to know what to work on next.
Pentests from multiple vendors affirmed a strong position but offered limited information and little to mitigate.
The Synack Red Team and the Synack Platform tested FDM’s web applications, host and cloud assets and APIs.
Detailed reports and direct access to testers helped developers reproduce vulnerabilities and informed development.
London-based FDM Group is a global leader in the recruit, train and deploy sector, equipping thousands of IT and business professionals every year to work with clients around the world. To assure customers and shareholders, it must keep its IT systems updated and free from the threat of a breach.
Cybersecurity is embedded in every part of the company. As part of its security and privacy-by-design philosophy, every consultant is trained in cybersecurity through trainer-led workshops and internal phishing campaigns.
FDM’s program included multiple vendors conducting pentests, but the results were not as expected. Patrick Wake, Group Director of Information Security, turned to human-powered penetration testing by Synack to prevent future vulnerabilities, inform the development process and improve procedures.
While our strong position was affirmed, it didn’t provide any intelligence about what to work on, and there is no such thing as zero percent chance of a breach. We needed to dig deeper to understand how we could be even more preemptive.
For a lean organization with an advanced security stance, Wake needed guaranteed experts who could move as fast as FDM does.
High standards for entry gave Wake confidence to trust the SRT with FDM’s most valuable assets. According to the 2023 case study, the SRT was a community of 1,500 researchers from 90 countries, and only 6% of applicants made the cut.
Synack started testing without a long lead time, giving FDM quick access to its pool of vetted researchers.
Synack handled researcher discussions and payouts, so FDM’s team could focus on mitigating findings.
Developers could talk directly with testers and watch a recording of how each vulnerability was found.
“When we’re trying to replicate a scenario, the video and in-depth diagrams were really well received and not something that’s conducted by all security testing companies.”
Synack added a layer of expert testing alongside FDM’s own internal vulnerability testing.
It all boils down to trust, because when you’re relying on an organization to pentest your network, you’re giving them access to your most valuable assets.
Synack can spin up very quickly without a huge lead time, and rather than a handful of testers, SRT offers hundreds of experts that can react very quickly.
We want to focus on mitigating findings, not managing the pool of money for payouts or determining which findings are actually exploitable.
Synack is the safety net to ensure that we have captured every possible issue, making it much more likely that everything is covered that can be.
Synack has the expertise that allows us to trust that we’ve done our jobs correctly. That’s invaluable.
Videos, in-depth diagrams and direct access to testers helped developers replicate each scenario and fix it.
Fast, flexible testing kept pace with FDM’s agility and sense of urgency.
Proactive security insights informed more robust development processes.
Findings moved through triage, mitigation and longer-term review by the infrastructure team.
The Attacker Resistance Score helped Wake evaluate time to remediation and whether fixes were successful.
FDM Group is a London-based global leader in the recruit, train and deploy sector, equipping thousands of IT and business professionals every year to work with clients around the world.
Pentests from multiple vendors had offered little actionable intelligence. FDM wanted vetted experts who could find exploitable vulnerabilities and show how to be more preemptive.
Web applications, host assets, cloud assets and APIs, tested by the Synack Red Team through the Synack Platform.
According to the 2023 case study, only about 6% of applicants were accepted, and researchers went through extensive testing before they could join the SRT.
FDM ran its own internal vulnerability testing, and Synack added a layer of expert testing alongside it, making it much more likely that everything that could be covered was covered.
Read the full two-page story of how FDM Group turned pentest findings into fixes with vetted researchers and reproducible evidence.
 Case Study · Travel technology How Sabre Builds Human-Led API Security Testing into Its Development Cycle Read the Sabre story →
 Case Study · Oil and gas How NOV Found Exploitable Vulnerabilities It Could Act On Read the NOV story →
 Case Study · Financial services How Varo Bank Used Continuous Pentesting to Demonstrate Security Readiness Read the Varo Bank story →