

Synack Managed Bug Bounty: Human-Led Testing at a Fixed Cost
Keep the creative, human-led research that makes bug bounty valuable, without unpredictable spend, an unvetted crowd or unattributed traffic. Synack runs the program with the Synack Red Team, triages every finding before it reaches your team and shows you exactly what was tested.
A bug bounty program you can budget for and verify
Fixed, predictable cost
One all-inclusive annual price replaces the platform fee, triage fees, bounty pool and per-bounty fees, with no surprise spend when researcher activity spikes.
Fully managed program
Synack runs the program with you and manages researcher engagement against your coverage goals, with a weekly or fortnightly CSM or TAM cadence.
Vetted researchers
Testing comes from the Synack Red Team: more than 1,500 background-checked researchers who pass a rigorous vetting process.
Coverage you can prove
See researcher hours and testing traffic across your scope, so you know critical assets get full, regular attention.
Triage and retesting included
Every finding is confirmed exploitable, documented with proof of concept and de-duplicated. Unlimited patch verification is included.
Control through LaunchPoint
All researcher traffic comes from known Synack IP sources, with push-button stop, start and pause, and every action logged.
How it compares with a traditional bug bounty
The same human-led research, without the unpredictable spend, unvetted crowd and operational burden of an open program.
Traditional bug bounty
Platform fee, bounty pool and triage fees that spike with researcher activityAn open, largely anonymous crowdYour team sets and chases bounties and triages reportsPer-retest fees or manual re-checksUnattributed traffic, limited ability to pause, data exposed to an open crowd
Synack Managed Bug Bounty
One fixed, all-inclusive annual priceMore than 1,500 background-checked Synack Red Team researchersSynack owns program management and researcher engagementEvery submission triaged, unlimited patch verification includedKnown-source traffic, push-button control and customer data kept within Synack's security boundary through LaunchPoint+
Questions about Synack Managed Bug Bounty
What is Synack Managed Bug Bounty?+
A fully managed bug bounty program delivered on the Synack Platform by the Synack Red Team, a private community of more than 1,500 background-checked researchers. Synack runs the program, triages every finding and reports on coverage, all for one fixed annual price.
How is it different from a traditional bug bounty?+
Traditional programs combine a platform fee, bounty pool and triage fees with an open, largely anonymous crowd that your team manages. Managed Bug Bounty uses vetted researchers, one fixed price, Synack-run triage with unlimited patch verification, known-source traffic you can pause, and analytics that show what was tested.
What is included in the fixed annual price?+
Triage of all submissions by Synack personnel, unlimited retesting, managed researcher engagement and incentives, LaunchPoint controlled traffic, coverage and test analytics with Attacker Resistance scoring, audit-ready reporting, liability coverage and a risk-based scope.
Who tests my assets?+
Synack Red Team researchers: more than 1,500 background-checked researchers who pass a rigorous vetting process, with technical and regional diversity. It is a private, trusted community, not an open marketplace.
Can I control or pause testing?+
Yes. All testing flows through LaunchPoint, Synack's secure gateway, from known Synack IP sources. You can schedule outage windows, such as a retail freeze, and stop, start or pause all testing at the push of a button.
How is my data protected?+
Every engagement runs on Synack-controlled infrastructure, and all researcher activity is logged and auditable. LaunchPoint+ gives the Synack Red Team the access they need while keeping customer data within Synack's security boundary.
Does it work with my existing security tools?+
Yes. Managed Bug Bounty runs on the same Synack Platform as Synack's human-led and AI pentesting. Ingest assets and vulnerabilities from tools such as Tenable and Qualys, sync tickets with Jira or ServiceNow, push data to Splunk and other SIEM tools, and set role-based access by team.
Can I see Synack Managed Bug Bounty in action?+
Yes. Take the Managed Bug Bounty interactive demo to see how you move assets into managed testing, schedule or pause testing windows, review validated findings, track coverage analytics and request patch verification. No sign-up is needed.
Can I add a VDP or AI testing?+
Yes. You can add a fully managed Vulnerability Disclosure Program for public submissions, with every report triaged and retesting included. You can also add Sara, Synack's agentic AI, to extend attack surface coverage, with findings validated by Synack before they reach your team.
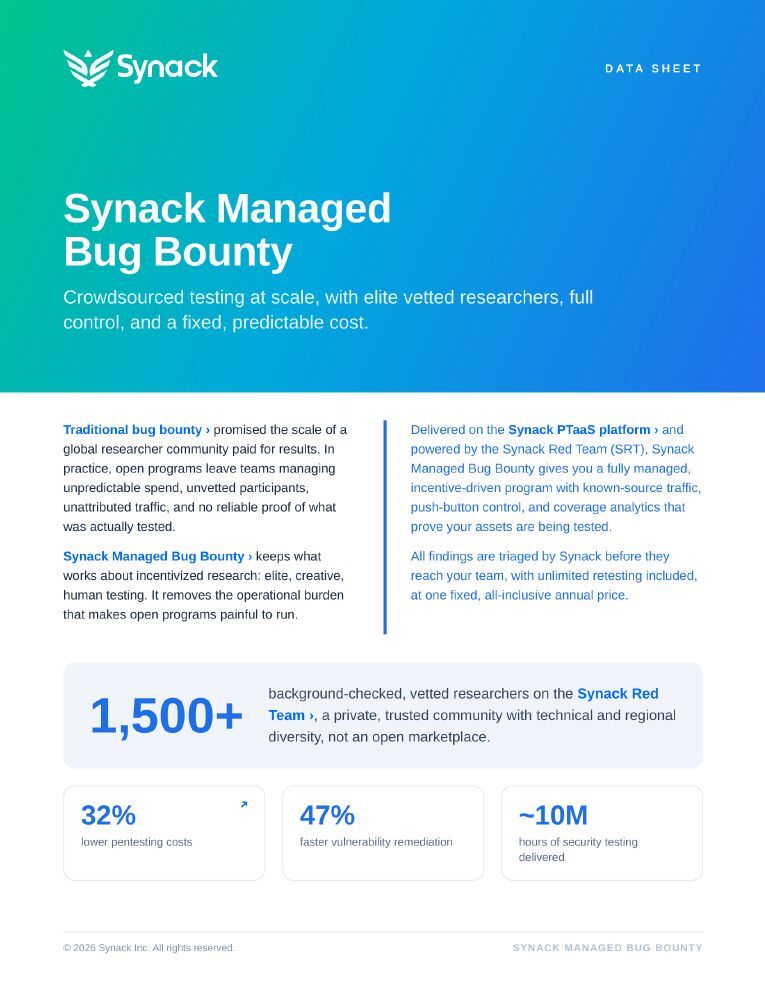
Get the Synack Managed Bug Bounty data sheet
Explore seven pages covering the managed program, what's included in the fixed price, LaunchPoint controls and how it compares with a traditional bug bounty.