
01 · The challenge
Scale and speed outpaced annual tests
With 800,000 employees, 10% annual turnover and code shipping continuously, compliance pentesting alone could not cover a global attack surface.
 Case Study
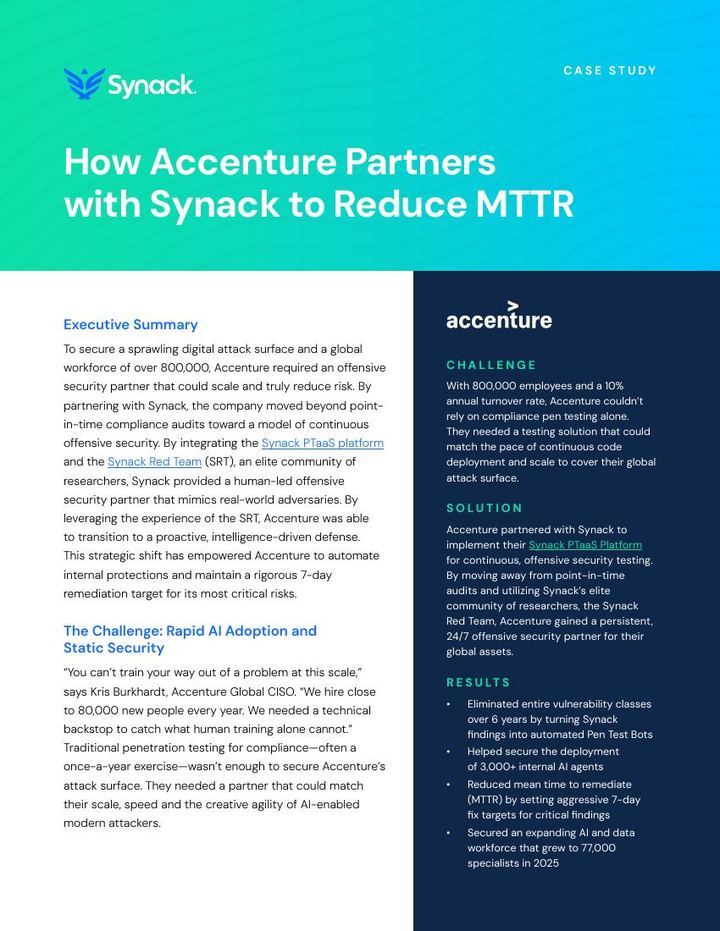
Annual compliance testing could not keep pace with continuous code releases and fast AI adoption across Accenture’s global attack surface. Continuous offensive security with the Synack Red Team helped it eliminate entire vulnerability classes and hold a 7-day remediation target for critical findings.
At Accenture’s scale, a once-a-year pentest leaves too much unseen between tests.
With 800,000 employees, 10% annual turnover and code shipping continuously, compliance pentesting alone could not cover a global attack surface.
Accenture moved to continuous testing on the Synack Platform, with the Synack Red Team testing its global assets around the clock.
Findings became automated checks that removed whole vulnerability classes, and critical issues are held to a 7-day fix target.
Accenture brings in close to 80,000 new people every year. Training alone cannot close the gaps that creates, and a single annual pentest cannot cover an attack surface that changes every day.
AI adoption raised the stakes. In two years, Accenture grew its AI and data workforce from 40,000 to 77,000 and delivered more than 6,000 advanced AI projects in fiscal 2025 (CRN, 2025).
Global CISO Kris Burkhardt needed testing that could match the pace of continuous deployment and scale across assets worldwide.
You can’t train your way out of a problem at this scale.
Accenture treats every Synack finding as a lesson for the whole organization. Patterns across findings show where systemic weaknesses sit.
Synack Red Team researchers surfaced issues such as unauthenticated objects buried in complex web applications.
Accenture’s team built internal automated scanners, called PenBots, that hunt for the same vulnerability class across the whole estate.
Ongoing testing catches new risks in new or sensitive systems and stops fixed flaws from quietly returning.
“Synack found these needles in the haystack.”
With more than 3,000 internal AI agents deployed and teams releasing code every hour, continuous testing acts as a safety net for fast-moving development.
The fun part of AI is enablement; the not-so-fun part is defending against AI-powered attacks.
You have to move at AI speed. Continuous testing ensures that as our teams release code every hour, we aren’t unknowingly reintroducing old flaws.
We don’t just want to fix a bug; we want to make the organization smarter. Synack helps us learn from our mistakes so we don’t repeat them.
Over six years, Accenture turned Synack findings into automated PenBots that remove whole classes of flaws, not single bugs.
Helped secure the deployment of 3,000+ internal AI agents.
Reduced mean time to remediate by holding critical findings to an aggressive 7-day remediation target.
Secured an AI and data workforce that grew to 77,000 specialists in 2025.
Instead of vulnerability counts, Burkhardt shows leadership falling MTTR and fewer recurring vulnerabilities through Synack Platform reporting, linking security investment to business goals.
Accenture is a global solutions and services company that helps enterprises reinvent by building their digital core and applying AI across the business, with approximately 786,000 people.
The Synack Platform for continuous, offensive security testing (pentesting as a service), with the Synack Red Team providing 24/7 testing across Accenture’s global assets.
PenBots are internal automated scanners Accenture built from Synack findings. Each one hunts for a vulnerability class Synack researchers found, across the whole environment, so the same flaw does not reappear elsewhere.
Through governance and organizational risk rather than vulnerability counts. Synack Platform reporting shows mean time to remediate falling and recurring vulnerabilities being prevented.
With thousands of internal AI agents and code released every hour, continuous testing catches new risks quickly and makes sure fixed flaws are not reintroduced.
See how Accenture eliminated vulnerability classes, helped secure 3,000+ internal AI agents and holds a 7-day remediation target for critical findings.