

SynackST and ST+: Human-Led Compliance Pentesting
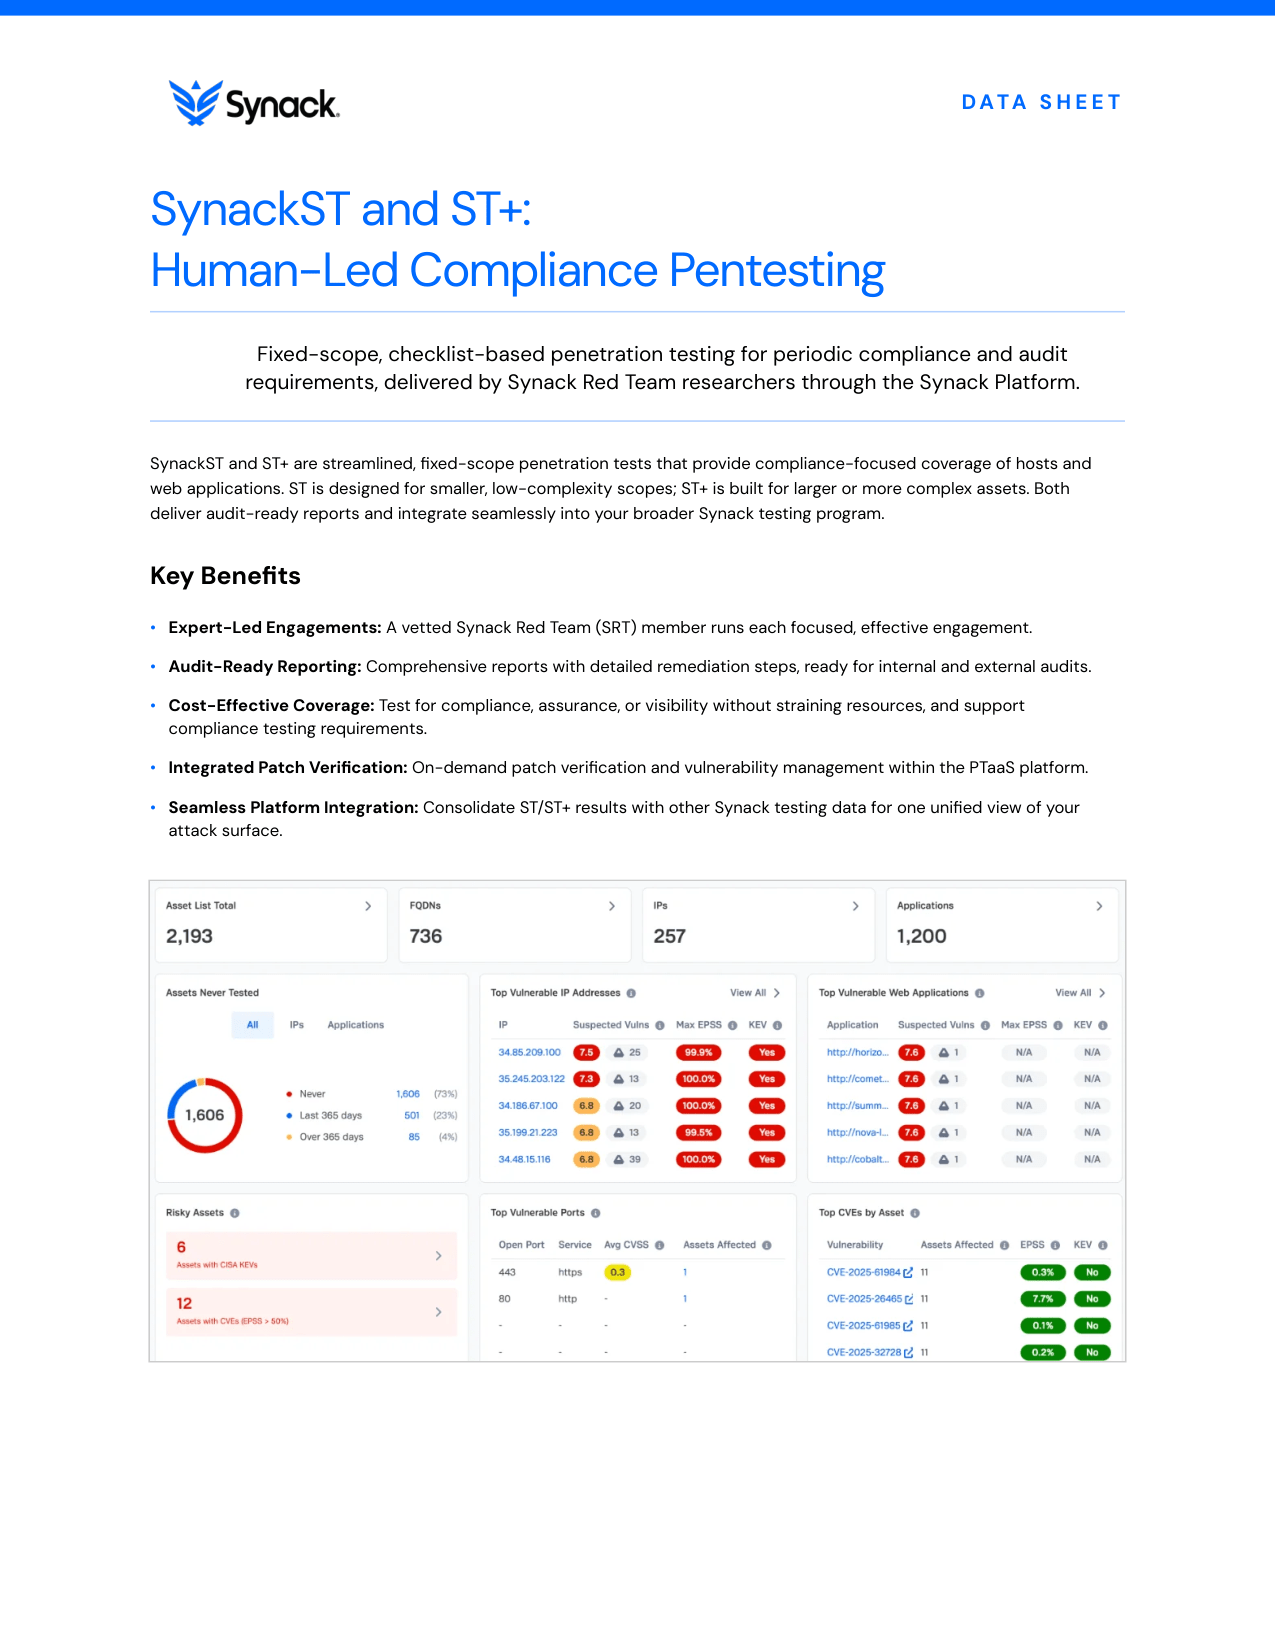
Support periodic compliance and audit requirements with fixed-scope penetration testing of web applications and hosts. SynackST and ST+ combine testing by a vetted Synack Red Team researcher with audit-ready reporting and patch verification through the Synack Platform.
Focused testing to support your next audit
Expert-led assessments
A vetted Synack Red Team researcher tests your agreed scope using a guided checklist.
Reporting for audit preparation
Receive findings with severity, impact and remediation guidance to support internal and external reviews.
Verification through the platform
Track findings and request patch verification through the Synack Platform, alongside your broader testing program.
Choose the scope that fits your assets
SynackST and ST+ provide periodic, fixed-scope testing for web applications and host infrastructure. Choose the assessment that fits the size and complexity of your agreed scope.
SynackST
Designed for smaller, less complex web applications and host environments. Unauthenticated web application scopes cover up to 25 URLs; host scopes cover up to 100 IPs.
SynackST+
Designed for larger or more complex web applications and host environments. Unauthenticated web application scopes cover up to 50 URLs; host scopes cover up to 250 IPs.
Questions about SynackST and ST+
What is the difference between ST and ST+?+
ST is designed for smaller, less complex scopes. ST+ supports larger or more complex web applications and host environments. The data sheet explains the scope limits and typical fit for each offering.
Who performs the testing?+
Each assessment is delivered by one vetted Synack Red Team researcher through the Synack Platform.
What does the assessment include?+
Testing follows a guided checklist for the agreed scope. Deliverables include a report with findings, severity, impact and remediation guidance, plus patch verification through the platform.
How does this support compliance?+
The assessments provide testing evidence and reporting to support periodic compliance requirements and audit preparation. The appropriate scope depends on your assets and applicable requirements.
Get the ST and ST+ compliance pentesting data sheet
Explore four pages covering assessment delivery, reporting, web application and host testing, and scope limits for ST and ST+.