

Sara AI Pentesting
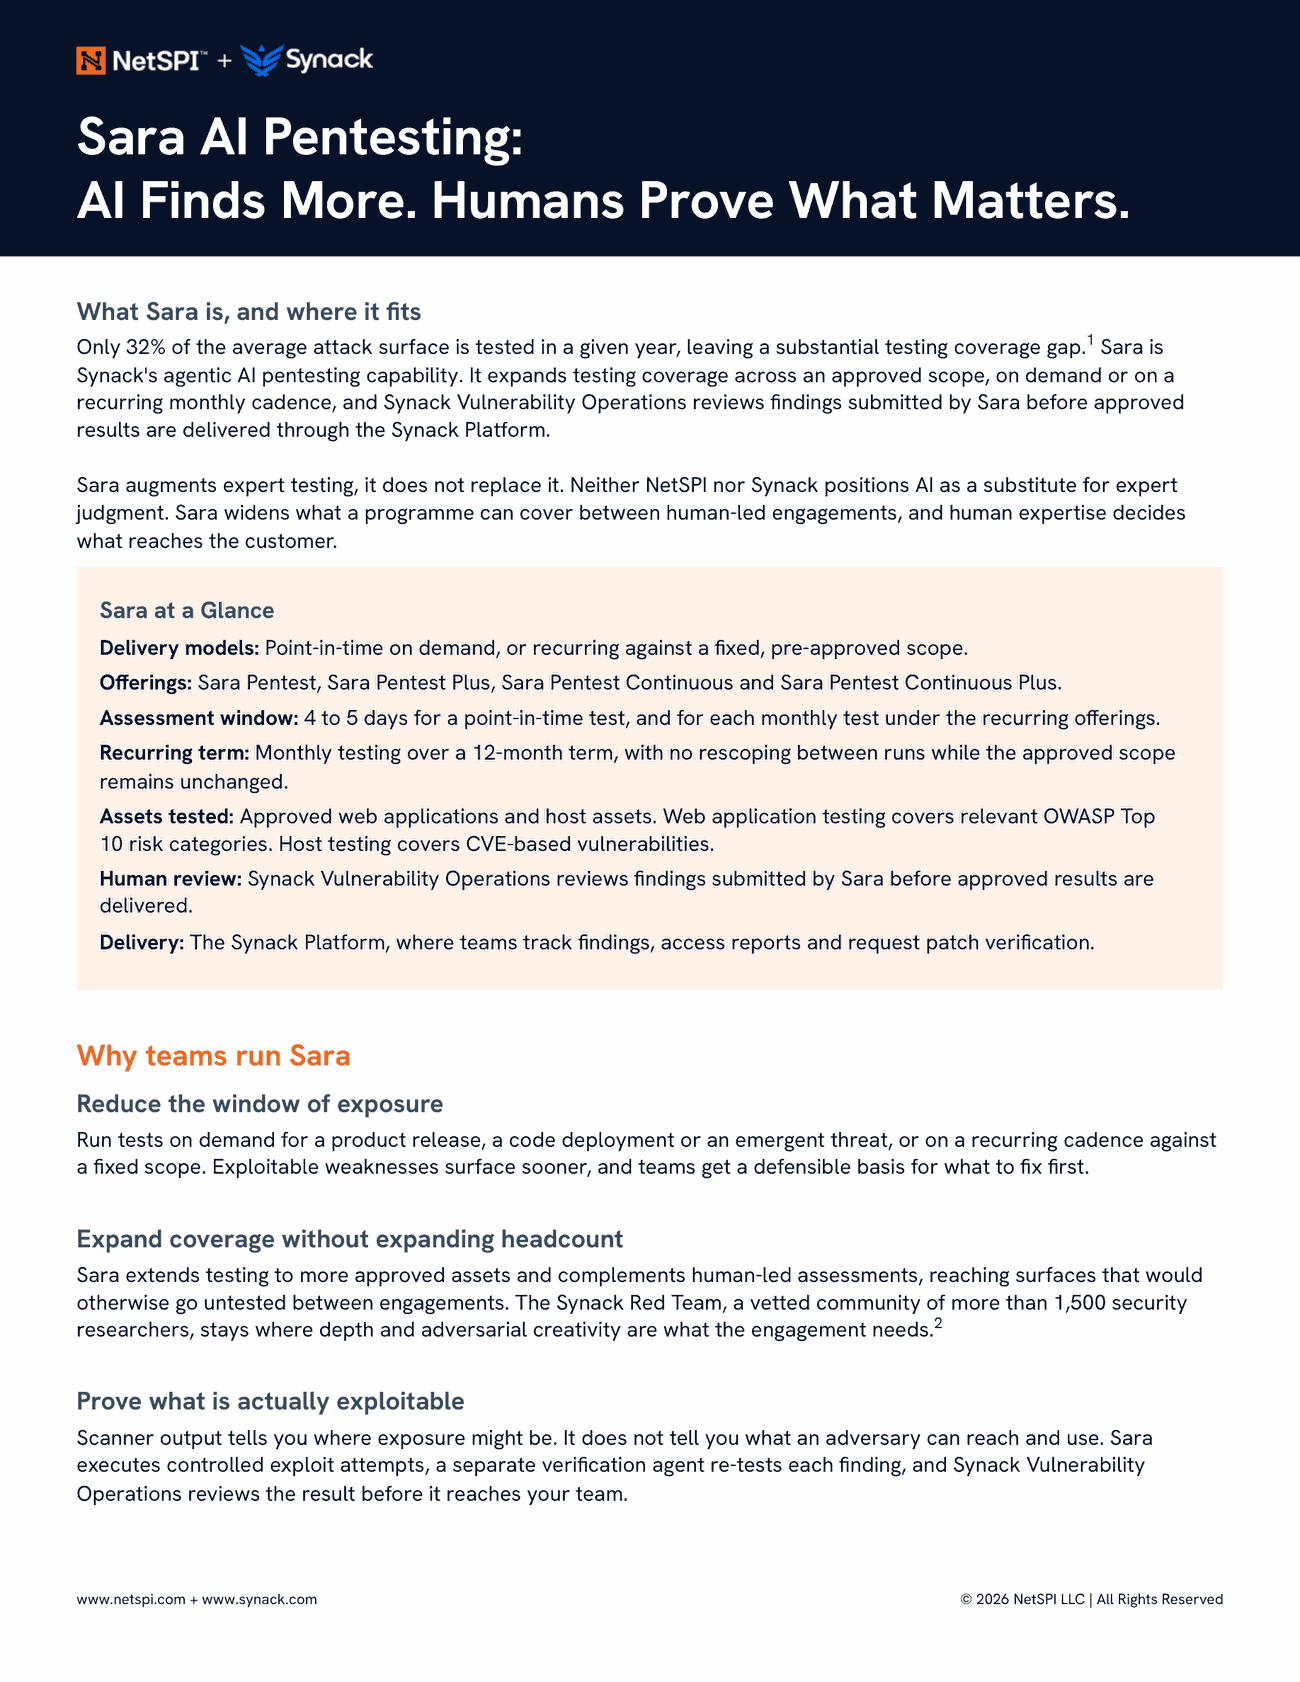
Only 32% of the average attack surface is tested in a given year. Sara, Synack's agentic AI pentesting capability, expands testing coverage across your approved scope, on demand or on a recurring monthly cadence. Synack Vulnerability Operations reviews findings submitted by Sara before approved results are delivered through the Synack Platform. This data sheet is published in the NetSPI and Synack joint identity.
Expand coverage. Repeat testing. Act on findings.
Extend your testing coverage
Sara tests more of your approved web applications and host assets, complementing human-led assessments rather than replacing them. Coverage reaches assets that would otherwise go untested between engagements.
Choose your testing cadence
Run a scoped assessment on demand for a release, a code deployment or an emergent threat, or test a fixed, pre-approved scope every month with Sara Pentest Continuous or Sara Pentest Continuous Plus.
Put findings to work
Approved findings arrive with evidence of exploitability and specific remediation guidance. Teams can request patch verification and export findings to connected systems through the platform.
Two ways to run Sara
Choose the approach that fits your testing needs, from a single assessment to recurring testing across an approved scope.
Point-in-time, on demand
Launch a scoped test for a product release, code deployment or emergent threat, with a 4 to 5 business day assessment window. Sara Pentest: 1 small authenticated web application, or 1 unauthenticated web application. Sara Pentest Plus: 1 medium or large authenticated web application, or 5 unauthenticated web applications, or 100 unauthenticated IPs.
Recurring, fixed scope
The same agentic AI process on a recurring monthly cadence over a 12-month term, against a fixed, pre-approved scope. No rescoping between runs while the approved scope remains unchanged. Sara Pentest Continuous: 1 small authenticated web application, or 10 unauthenticated web applications. Sara Pentest Continuous Plus: 1 medium or large authenticated web application, or 25 unauthenticated web applications, or 100 unauthenticated IPs.
Questions about Sara AI Pentesting
What assets can Sara test?+
Approved web applications and host assets. Web application testing covers relevant OWASP Top 10 risk categories, including SQL injection, cross-site scripting, SSRF, and broken authentication and access control. Host testing covers CVE-based vulnerabilities. Scope is set by the offering you select, from a single authenticated web application to multiple unauthenticated applications or IPs.
What is the difference between the point-in-time and recurring offerings?+
Sara Pentest and Sara Pentest Plus are point-in-time assessments you launch on demand, each with a 4 to 5 day assessment window. Sara Pentest Continuous and Sara Pentest Continuous Plus run the same agentic AI process on a recurring monthly cadence over a 12-month term, against a fixed, pre-approved scope, with a 4 to 5 business day window for each monthly test. The Plus offerings cover a larger scope at each tier.
How much is included in each offering?+
Sara Pentest: 1 small authenticated web application, or 1 unauthenticated web application. Sara Pentest Plus: 1 medium or large authenticated web application, or 5 unauthenticated web applications, or 100 unauthenticated IPs. Sara Pentest Continuous: 1 small authenticated web application, or 10 unauthenticated web applications. Sara Pentest Continuous Plus: 1 medium or large authenticated web application, or 25 unauthenticated web applications, or 100 unauthenticated IPs.
Where does human review take place?+
Within the Synack Platform workflow. Synack Vulnerability Operations reviews findings submitted by Sara before approved results are delivered to customers.
What does a Sara report include?+
An executive summary and engagement details, a vulnerability list with categorization and severity distribution, a description, severity and impact analysis for each verified finding, steps to reproduce with evidence of exploitability, and specific remediation recommendations. Separately, in the Synack Platform, teams can request patch verification and export findings to connected systems.
How do NetSPI + Synack combine AI and human expertise?+
Sara expands testing coverage with agentic AI across point-in-time and recurring assessments, while expert testers provide the depth, business context and adversarial creativity needed for more complex testing. Together, NetSPI + Synack combine AI-driven scale with human expertise to help customers identify what is actually exploitable and prioritize what matters most.
Get the Sara AI Pentesting data sheet
Two pages covering all four offerings and their included scope, the four-phase agentic AI process, where Synack Vulnerability Operations reviews findings, and what every Sara report contains. Published in the NetSPI and Synack joint identity. No form, no email required.