

NetSPI and Synack: Continuous Offensive Security at AI Scale
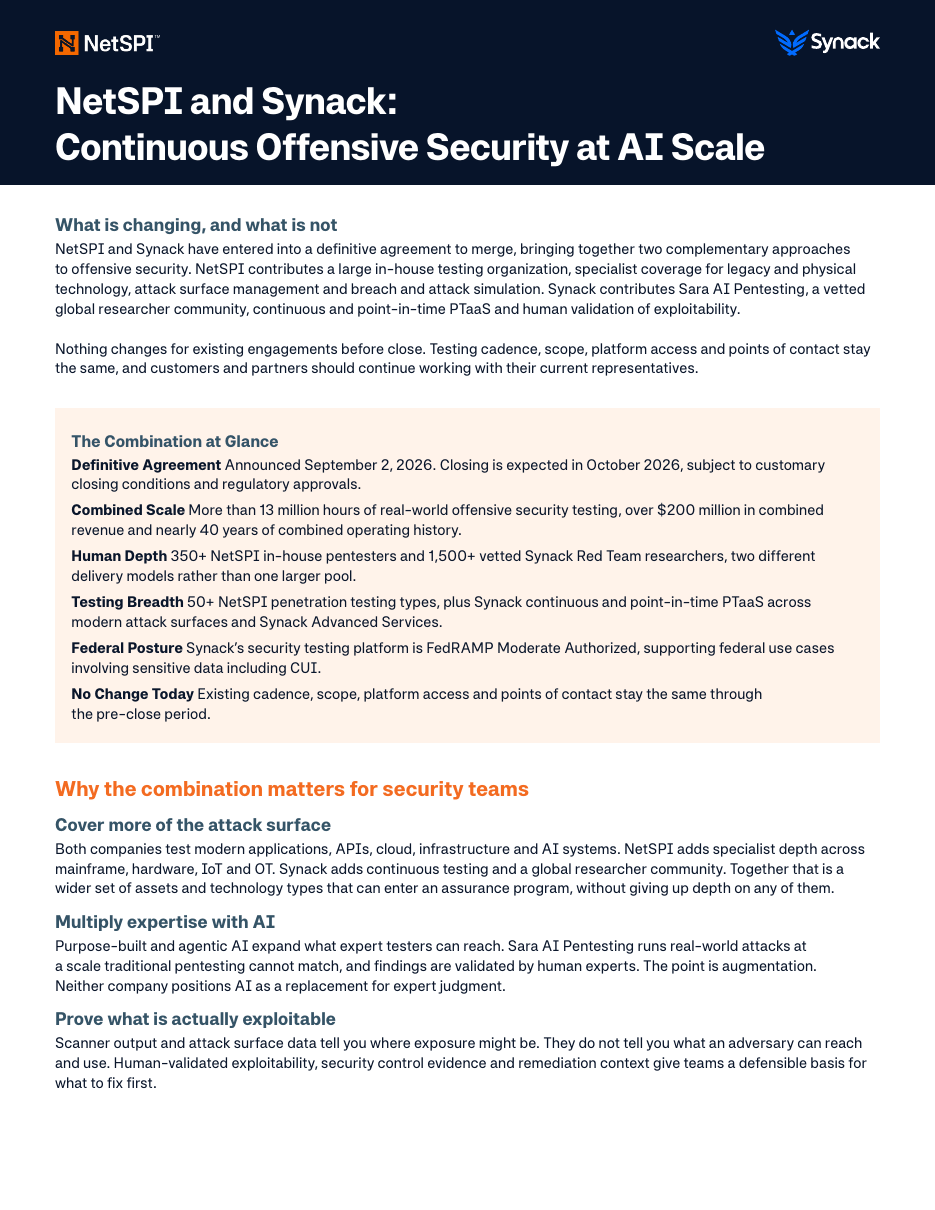
NetSPI and Synack have joined forces to deliver continuous offensive security at AI scale. Together, in-house specialists, Sara AI Pentesting and the vetted Synack Red Team expand coverage across your attack surface and validate what is exploitable. Explore what the combined expertise means for your security testing program.
What the combination means for security teams
Cover more of the attack surface
NetSPI and Synack both test applications, APIs, cloud, infrastructure and AI systems. NetSPI adds specialist depth across mainframe, hardware, IoT and OT. Synack adds continuous testing and a global researcher community.
Multiply expert testing with AI
Sara AI Pentesting runs real-world attacks at scale, and human experts validate the findings. AI extends what expert testers can reach. It does not replace their judgment.
Prove what is actually exploitable
Human-validated exploitability, control evidence and remediation context give your team a defensible basis for what to fix first.
Complementary expertise. Broader security coverage.
Together, NetSPI and Synack bring more than 13 million hours of real-world offensive security testing. Continuous testing keeps changing attack surfaces under scrutiny, while specialist, compliance and point-in-time assessments stay where the technology, risk or regulation demands them.
NetSPI
350+ in-house pentesters across 50+ penetration testing types, including specialist coverage for mainframe, hardware, automotive, medical devices, IoT and OT, plus attack surface management and breach and attack simulation.
Synack
Sara AI Pentesting and 1,500+ vetted Synack Red Team researchers, delivering continuous and point-in-time PTaaS with human-validated findings, patch verification and a FedRAMP Moderate Authorized platform.
When did the NetSPI and Synack merger complete?+
The merger between NetSPI and Synack completed on October 5, 2026. Explore what the combined expertise means for security teams.
Does anything change for my current testing engagements?+
For questions about your testing cadence, scope, platform access or support, please contact your existing Synack or NetSPI representative.
How do the NetSPI and Synack testing models differ?+
The two approaches are complementary. NetSPI brings 350+ in-house pentesters and specialist teams for technology such as mainframe, hardware, IoT and OT. Synack combines Sara AI Pentesting with 1,500+ vetted Synack Red Team researchers for continuous and point-in-time testing, with human validation of exploitability.
Where can I learn about products, pricing and integration plans?+
Contact your Synack or NetSPI representative for the latest information on available offerings, pricing and integration plans.
What should partners do now?+
Contact your existing Synack or NetSPI partner manager for guidance on customer opportunities, available offerings and any changes to partner processes.
Get the NetSPI and Synack solution brief
Explore how NetSPI’s specialist testing expertise, Sara AI Pentesting and the vetted Synack Red Team complement each other to expand coverage and validate exploitable vulnerabilities.